HIDRA
A12 / iOS 18.7.2 — from AppleJPEGDriver UAF to kernel r/w.
Hidra is a research jailbreak project for iPhone XR (A12) on iOS 18.7.2. The kernel entry is CVE-2026-20687 in AppleJPEGDriver. The current rung is a controlled free and a same-type reclaim — not a jailbreak yet.
Crash → Control → Jailbreak
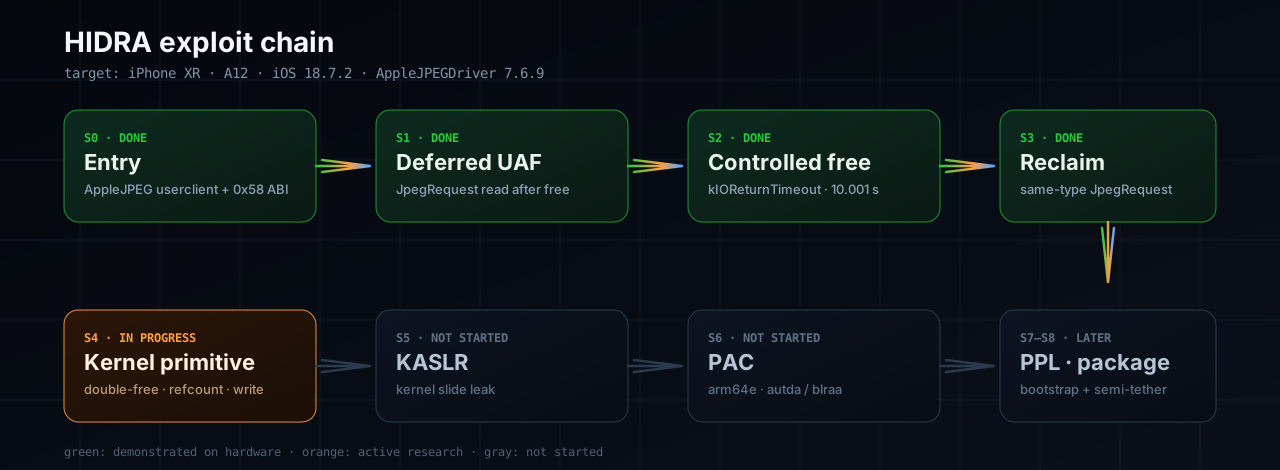
Green stages are demonstrated on hardware. Orange is active research. Gray is not started. The project does not claim kernel r/w until S4 is real.
Entry
AppleJPEGDriver userclient opens from the app sandbox; the 0x58 decode ABI works.
Deferred UAF
Freed JpegRequest is read by a later queue walk. far=0x308, poison 0xfeedface….
Controlled free
A true sync decode hits the 10 s wait: kIOReturnTimeout, dt=10.001s.
Same-type reclaim
Ten async requests after the timeout reuse the freed slot; the kernel survives.
Kernel primitive
Double-free, IOSurface/UC refcount corruption, or a write through the queue node.
KASLR
Standard leak surfaces are clean on 18.7.2. Needs a kernel read or side channel.
PAC
A12 is arm64e. The autda/blraa call blocks a naive fake vtable.
PPL / SPTM
Page tables and kernel text are protected. Needs a data-only or patch primitive.
Package
Semi-tethered bootstrap, package manager, recovery path. No public build yet.
How Hidra gets in
The entry is an app. The bug is a decoder timeout. The goal is a controlled kernel primitive, then KASLR/PAC/PPL, then a bootstrap.
1 · Entry
IOServiceOpen("AppleJPEGDriver", 0) from a sideloaded app. No entitlement required on this target.
2 · UAF
Async decodes + close, or a forced sync timeout, leave a freed JpegRequest in the per-codec queue.
3 · Primitive
Reclaim the slot with a same-type request, then turn the stale node into a double-free or write. This is the current gate.
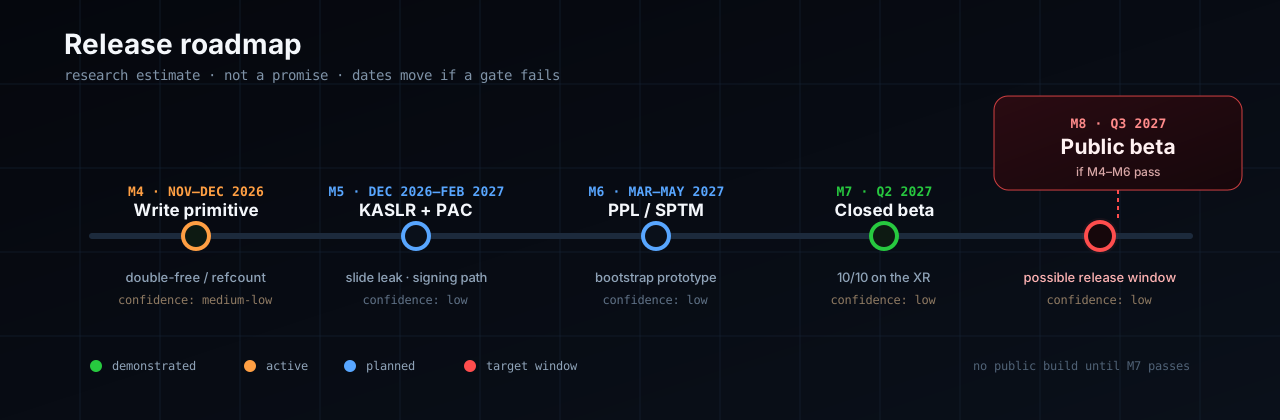
No promise. A target window.
The date is a research estimate. It moves if a gate fails. A build that only panics is not a release.
One device first
The project starts with the hardware we can test. Everything else is later.
| Device | SoC | iOS | State |
|---|---|---|---|
| iPhone XR (iPhone11,8) | A12 / T8020 | 18.7.2 (22H124) | PRIMARY |
| iPhone XS / XS Max | A12 | 18.7.x | UNTESTED |
| iPhone 11 / SE 2 | A13 | 18.7.x | UNTESTED |
| iPhone 12 and newer | A14+ | any | NOT INITIAL |
| iOS 18.7.7+ / 26.4+ | — | — | PATCHED |
FAQ
Is Hidra a working jailbreak?
No. It is the research project that aims to become one. The current state is a kernel UAF and a controlled same-type reclaim. There is no kernel r/w yet.
Which device is supported?
iPhone XR (A12) on iOS 18.7.2 is the primary test device. Other A12/A13 devices on 18.7.x are untested. iOS 18.7.7+ and 26.4+ are patched.
Is it tethered?
The first target is semi-tethered: the device boots normally, the user launches Hidra after a reboot, and the bootstrap is reapplied.
When will it be released?
Current estimate: closed beta Q2 2027, public beta Q3 2027, only if the write primitive, KASLR/PAC, and PPL stages pass. There is no promised date.
Will it bypass iCloud or activation locks?
No. Hidra targets owned devices with a normal sideloading setup. It does not bypass activation locks, iCloud locks, or MDM.
Why the name Hidra?
Hydra: many heads, many paths into the kernel. The project started with HID (IOHIDFamily) and continued through AppleJPEGDriver. The kernel entry stage is codenamed JPEGSWORD.
Everything is documented
The PoCs, panic logs, control ladder, and test matrix live in the research repository.